Somebody looked at Android's trust model and decided to weaponize it. Meet RatHat — a new AI-powered malware that dresses up as a legitimate Chrome download, then quietly turns your phone against your bank account. Three independent security firms flagged it this week, and the details are genuinely unpleasant.
That friendly download icon is the whole con. RatHat doesn't brute-force anything — it asks to be installed, disguised as Chrome, and lets you do the rest.
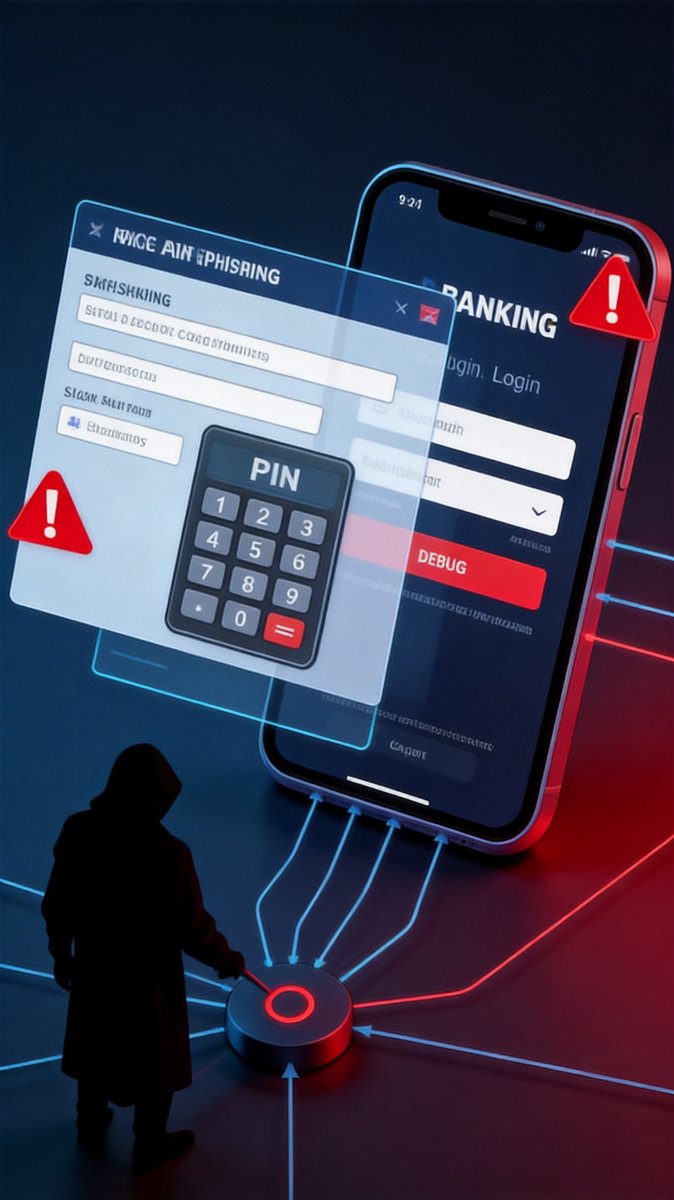
This is the overlay trick: a fake login window painted on top of your real banking app. You type your password into it. That's the entire theft — logins, PINs, shipped to attackers in real time.
And the part that earned the horror-movie treatment: RatHat abuses Android's own developer tools to survive an uninstall. You delete the app — it stays.
The playbook hasn't changed: stick to the Play Store, keep Play Protect on, and maybe stop sideloading sketchy APKs from random links. Google's Play Protect is playing catch-up on this one.
Watch the full breakdown:
▶ RatHat: the Android malware that robs your bank
Source: [CNET](https://www.cnet.com/tech/services-and-software/rathat-malware-attacks-android-phones/" target="_blank" rel="noopener")